Azure Bastion is a managed PaaS service that allows you securely connect to your virtual machines over a TLS connection. This connectivity can be established from the Azure portal or through a native client to the private IP address on the virtual machine. Advantages of using Bastion include:
- Azure virtual machines don’t need a public IP address. Connections are over TCP port 443 for HTTPS and can traverse most firewalls.
- Virtual machines are protected against port scanning.
- The Azure Bastion platform is constantly updated and protected against zero-day exploits.
With Bastion, you can control the RDP and SSH connectivity to your virtual machine from a single point of entry. You can manage individual sessions from the Bastion service in the Azure portal. You can also delete or force a disconnect of an on-going remote session if you suspect a user isn’t supposed to be connecting to that machine.
The following diagram shows the reference architecture for using Azure Bastion to protect Azure virtual machines.
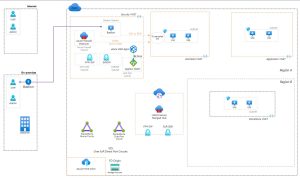
To protect your Azure virtual machine, deploy Azure Bastion and begin using RDP and SSH to connect to your virtual machines with their private IP addresses.