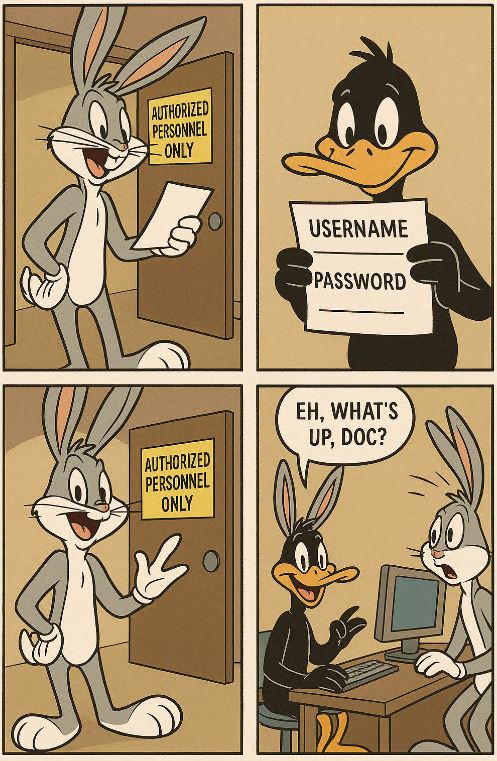
Cybersecurity doesn’t have to be dry. Sometimes, a couple of wisecracking cartoon characters can teach you more about authentication flaws than a 300-page manual. Let’s talk about one of the most common web security risks — Broken Authentication, also known as OWASP Top 10 – A2 — through the antics of Bugs Bunny and Daffy Duck.
🧠 What Is Broken Authentication?
Broken authentication refers to weaknesses in identity and session management that allow attackers to:
-
Compromise user credentials
-
Assume another user’s identity
-
Hijack active sessions
-
Access sensitive functions as someone else
This usually happens due to:
-
Poor password policies
-
Weak session handling (no expiration, no regeneration)
-
Credential stuffing or brute force vulnerabilities
-
Storing passwords in plaintext
-
Flawed implementation of login systems
🦆 The Scenario — Daffy’s Dirty Trick
In our cartoon comic:
-
Bugs Bunny has legitimate access to a secured zone labeled “AUTHORIZED PERSONNEL ONLY”.
-
Daffy Duck, as sneaky as ever, gets hold of Bugs’ username and password — probably found it scribbled on a sticky note or intercepted it via phishing (we’ll never know).
-
Daffy then disguises himself with fake Bugs ears, logs into the computer, and pretends to be Bugs:
“Eh, what’s up, doc?” -
The real Bugs shows up and is horrified — Daffy’s inside the system, impersonating him!
🔍 Real-World Equivalent
This is a classic case of Broken Authentication:
-
The system failed to verify that the user was truly Bugs Bunny.
-
Daffy used stolen credentials to gain access without any multi-factor authentication.
-
There were no checks in place to prevent session hijacking or unusual behavior.
🛡️ How to Prevent Broken Authentication
Let’s secure Bugs’ system — and yours:
| 🧰 Protection Measure | 💡 Description |
|---|---|
| ✅ Multi-Factor Authentication (MFA) | Require something more than username/password — like SMS or authenticator apps |
| 🔐 Strong Password Policies | Enforce complexity, rotation, and block commonly used passwords |
| 🚫 No Credential Reuse | Prevent login attempts from known breached credential sets |
| ⏱️ Session Expiration | Kill inactive sessions and regenerate session tokens after login |
| 📉 Brute Force Prevention | Add rate limiting and account lockouts |
| 🔎 Monitor & Log | Detect suspicious login patterns (e.g. Daffy logging in from Mars) |
🎓 TL;DR – What Bugs Bunny Teaches Us
Daffy Duck exploited a simple authentication weakness to impersonate someone else. Real attackers don’t need to wear rabbit ears — they’ll use bots, leaked credentials, and logic flaws to get in.
If your system can’t tell Bugs from Daffy — you have a problem.